Adware Empire - IronSource and InstallCore
Tracing a malicious Bing ad campaign through a Chrome download to adware, and the companies the IPs and payloads connect back to.

Tracing a malicious Bing ad campaign through a Chrome download to adware, and the companies the IPs and payloads connect back to.

A USPS-themed phishing PDF opens onto a researcher’s goldmine of phishing sites, hosted at a colocation provider with a pattern worth noting.

Following a SWIFT-themed spam email to a Box-hosted downloader scoring 0 of 63 on VirusTotal, and the evasion tactics that kept it there.

How misspelled domains funnel users into surveys, pop-ups and parked pages, and the advertising networks that make the whole arrangement pay.
Many people would rather ask a chatbot than a colleague. What that preference reveals about the cost of asking at work, and why useful help has to remember what actually worked.
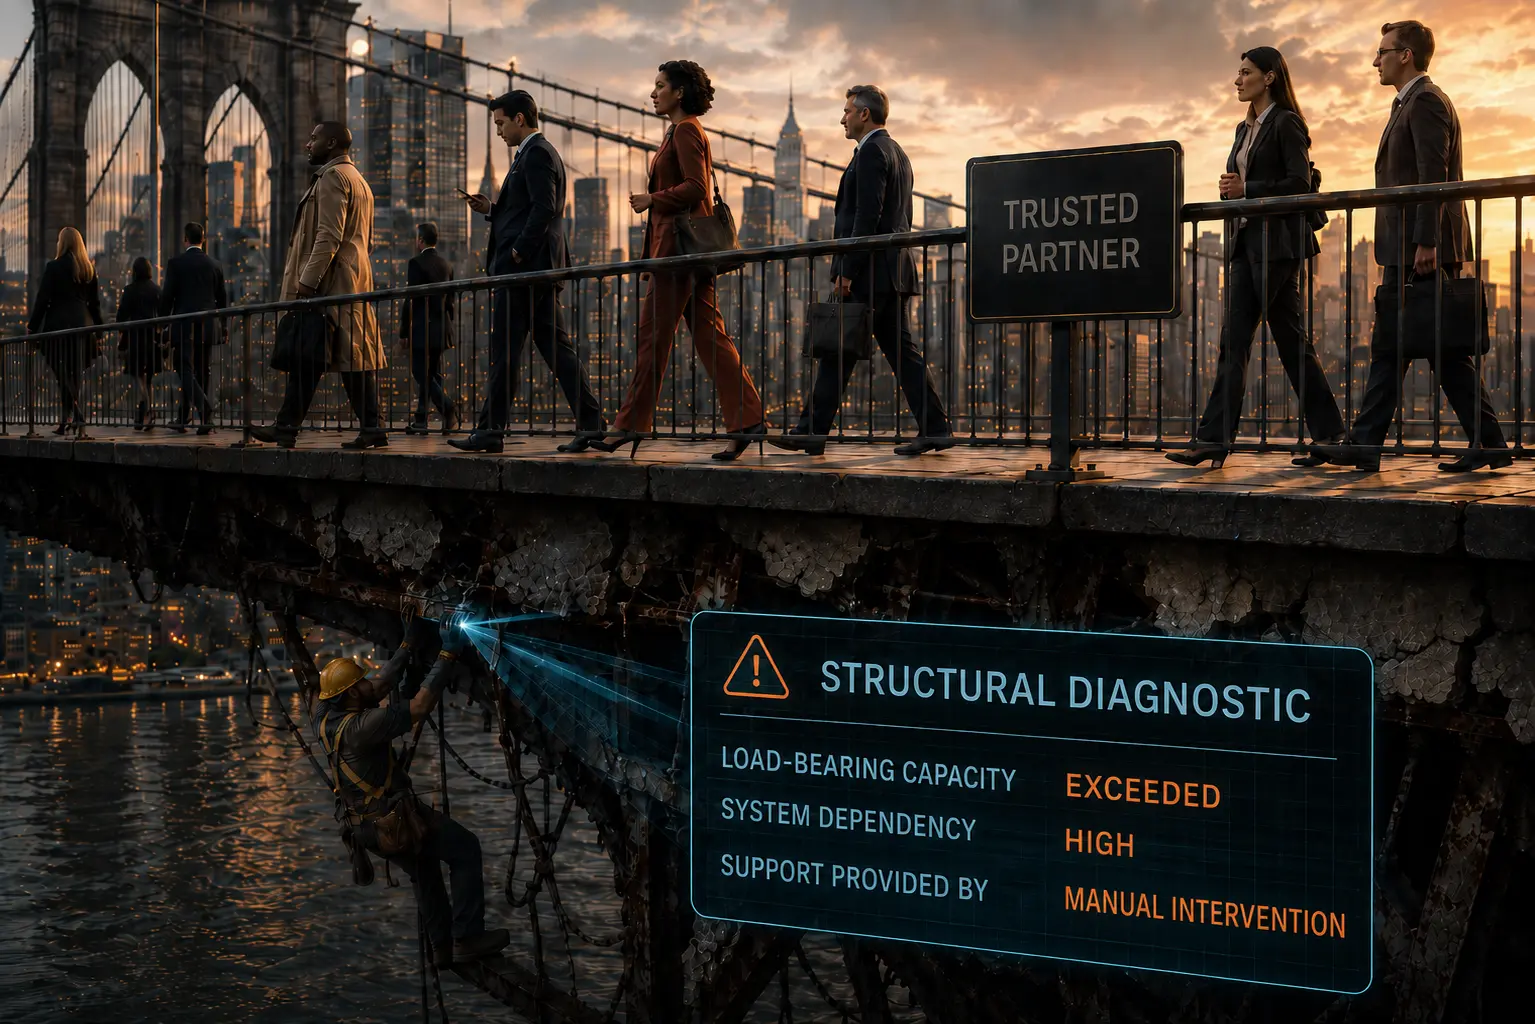
Why a company can look financially healthy and still be operationally insolvent: selling more responsibility than its systems can carry, and financing the gap with trust and the hidden labour of a few people.
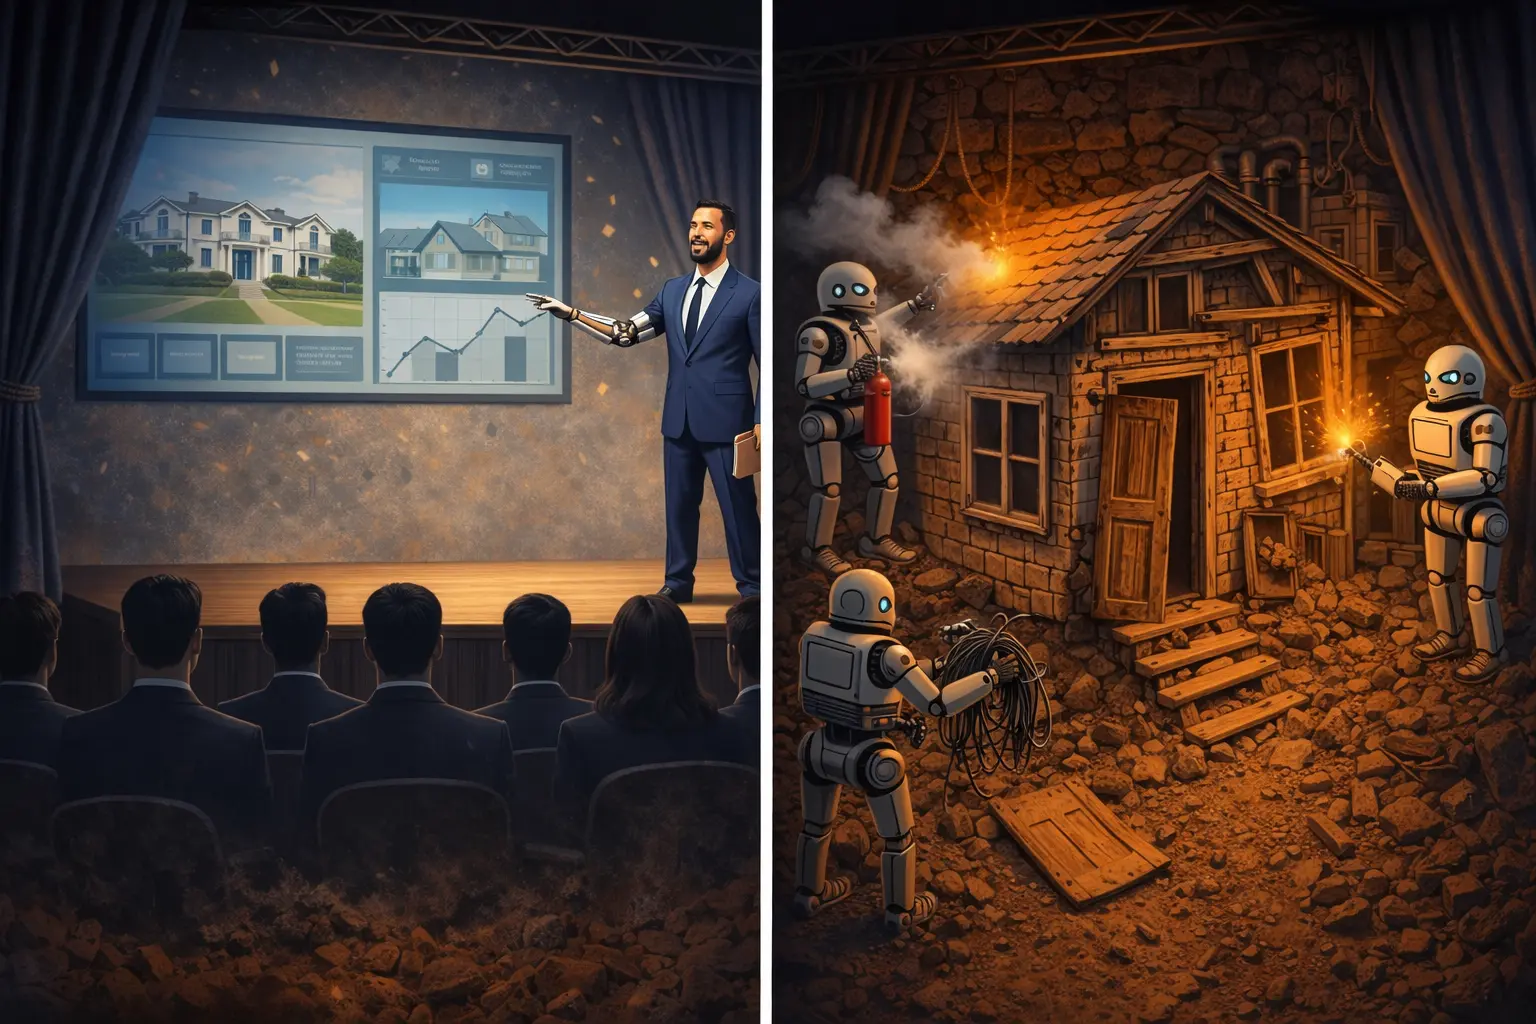
Modern SaaS rarely fails outright; it almost works. Why the real bottleneck is no longer writing code but understanding what is built, and how incomplete systems shift the burden onto customers.
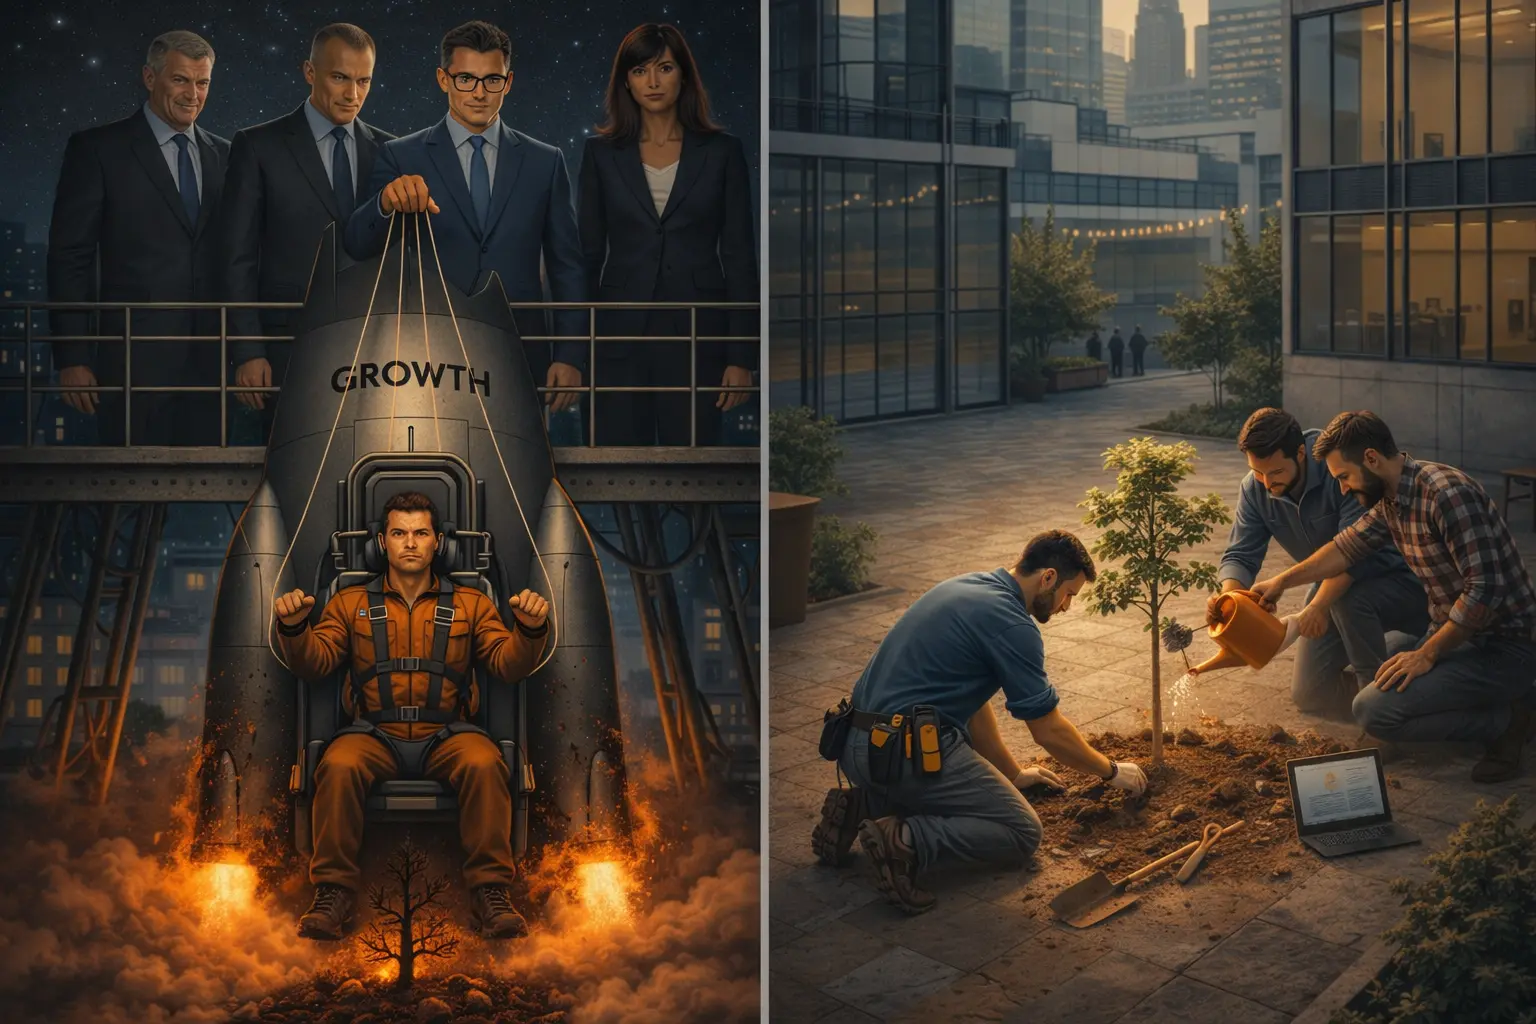
Companies rarely lose their soul overnight. How treating stewardship as inefficiency moves decisions away from the people who understand their consequences, and turns strategy into performance.
I have been taking computers apart since I was a teenager in the late 90s. It started with a Packard Bell, dial-up modems, and a program called Navigator that was meant to keep children out of parts of the system. I found a key combination that crashed it and dropped me on the desktop. That was the first time I understood that what a system is supposed to do and what it actually does are two different things, and I have been pulling at that thread ever since.
Growing up, I faced challenges within my family, as my brother occasionally stole the money I earned from web design and local computer support. Determined to protect what was rightfully mine, I purchased a large home safe, symbolizing my commitment to fortify my defenses. Despite his attempts to undermine me, his efforts only scratched the surface. I even suggested installing a hallway camera to bolster security, shaping my strategic mindset and the principle of protecting others from exploitation.
Throughout my career, I’ve maintained a balanced approach, embodying intensity, direction, and persistence to deliver consistent, high-quality service to every organization I work with. This dedication has led to self-concordance, job engagement, and an commitment to achieving goals. Over the past fifteen years, I’ve had the privilege of building, exploring, and developing security systems globally, likely safeguarding something that belongs to you along the way.
My writing, enriched by interviews with late 90s hackers like John Vransevich (JP), Kent Browne (Hack Phreak), Carolyn Meinel (Happy Hacker), Eric Ginorio (Bronco Buster), Marc Maiffret (sn1per), Jodi Jones (Venomous), and Patrick Gregory (MostHated), reflects my deep involvement in hacker culture. Beginning in my youth, this journey included interactions with the FBI and Secret Service, where I was more an inquisitive explorer than an adversary. My goal has always been to safeguard information integrity and confidentiality, steering clear of deceit or harm.
Contact me at the bottom of this page if you have any questions/comments about the blogs, or follow me on Linkedin
-Matthew
By subscribing, you’ll receive a monthly round-up of the latest news. There’ll be no spam, I promise :)